
Manage folder access
Control which Roles and users can access a folder, and use Permission sets to define what they can do.
Folder access can be granted in two ways:
- Roles with access – give multiple users access to the folder through a Role. This is the recommended method when users need the same access.
- Users with direct access – give an individual user access to the folder as a one-off exception.
Every folder assignment uses a Permission set to define what the Role members or individual user can do inside the folder.
Account Owners and Administrators always have access to all folders and are therefore not listed as normal folder permissions.
Open Folder access
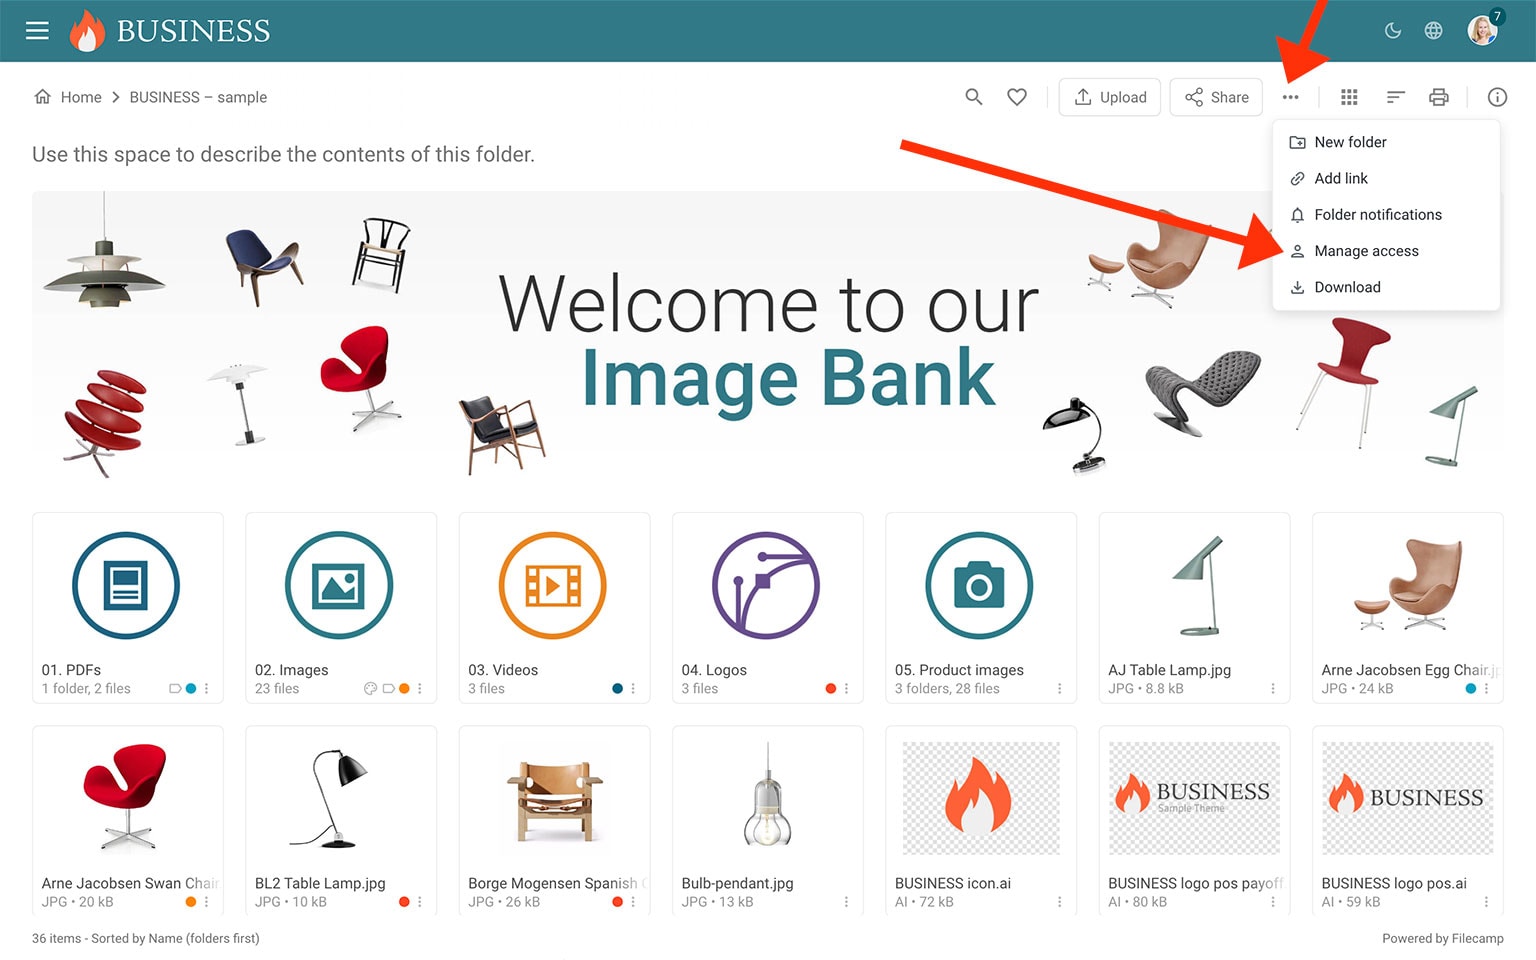
Open the folder, click the More icon (three dots) in the Toolbar, and select Manage access.
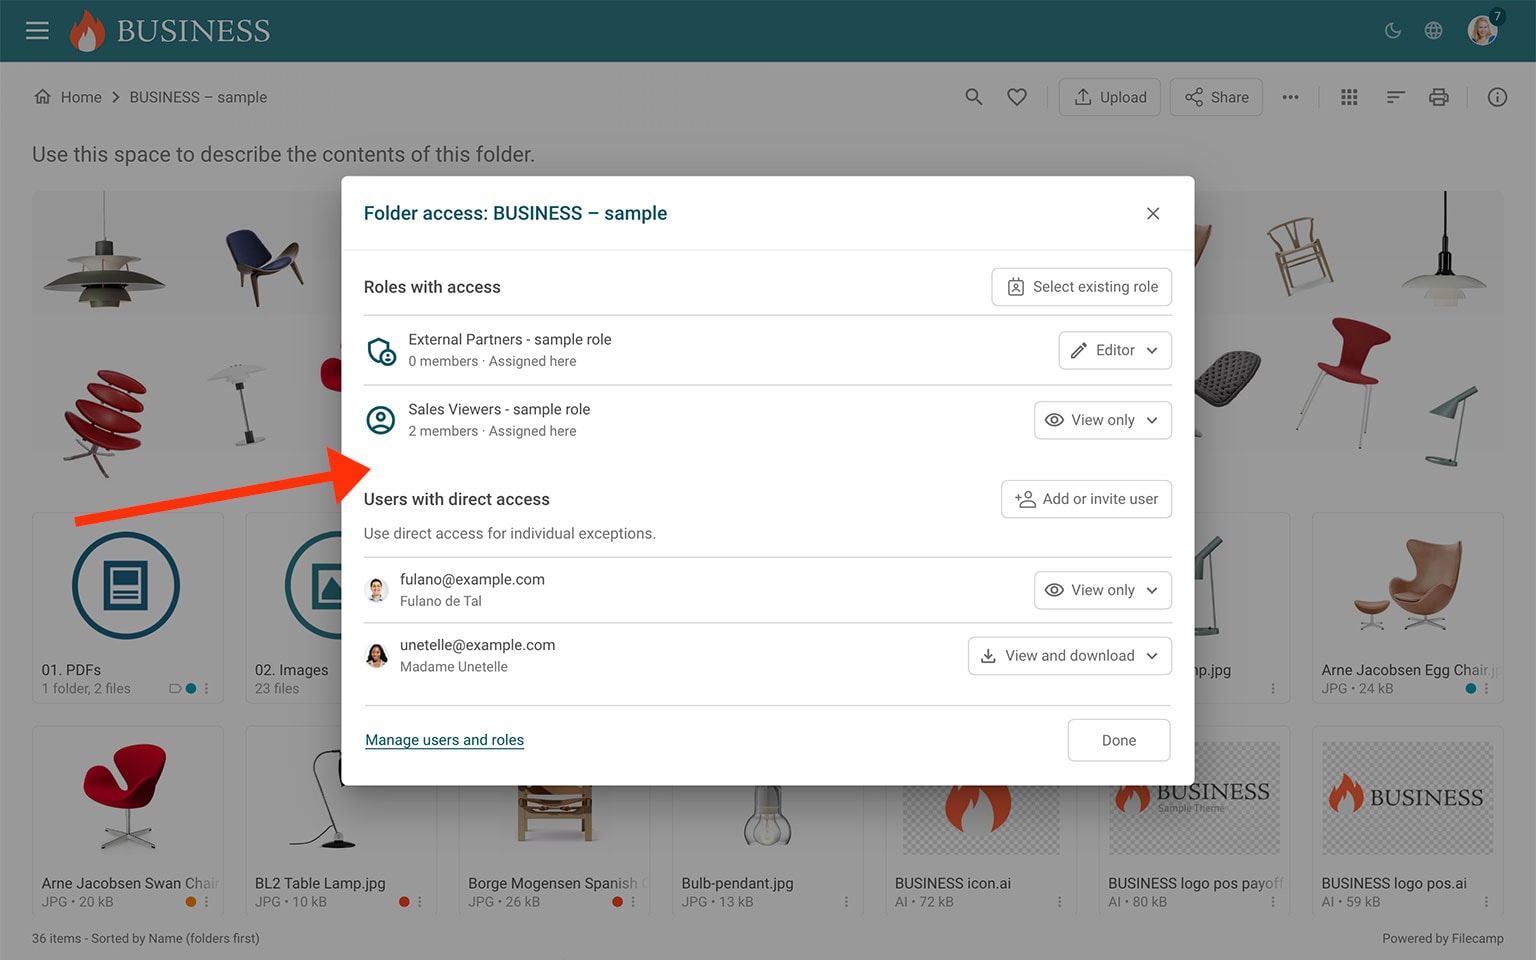
The Folder access window shows who can access the selected folder and which Permission set applies.
Access is divided into two sections:
- Roles with access
- Users with direct access
Roles with access
Roles with access lists the Roles that give their members access to the folder.
A Role can contain multiple users. When you give a Role access to a folder, every member of that Role receives access through the selected Permission set.
Roles are the recommended way to manage access for teams, departments, external partners, or other groups of users. They keep access consistent and make future changes easier to manage.
To give another Role access, click Select existing role, choose the Role, and select the Permission set that should apply.
Tip: If several users need the same folder access, use a Role instead of adding each user directly.
Users with direct access
Users with direct access lists individual users who have been given access to the folder directly.
Direct access is best for individual exceptions—for example, when one user needs access to a private folder that should not be included in a shared Role.
Each direct folder assignment uses a Permission set to define what the user can do inside the folder.
Tip: If the same access will be reused for several users, consider creating or using a Role instead.
Permission sets
Permission sets define what users are allowed to do inside folders they can access.
Filecamp includes three built-in Permission sets:
- View only – users can view files and folders but cannot download or share them.
- View and download – users can view and download files and folders but cannot share them.
- Editor – users can upload, edit, organize, share, and manage files and folders.
You can also create custom Permission sets containing the combination of permissions you need.
Tip: Roles define who receives access. Permission sets define what they can do.
Permission sets can be created and managed from Admin > Users > User settings > Permission sets.
Read more about Permission sets.
Change a Permission set
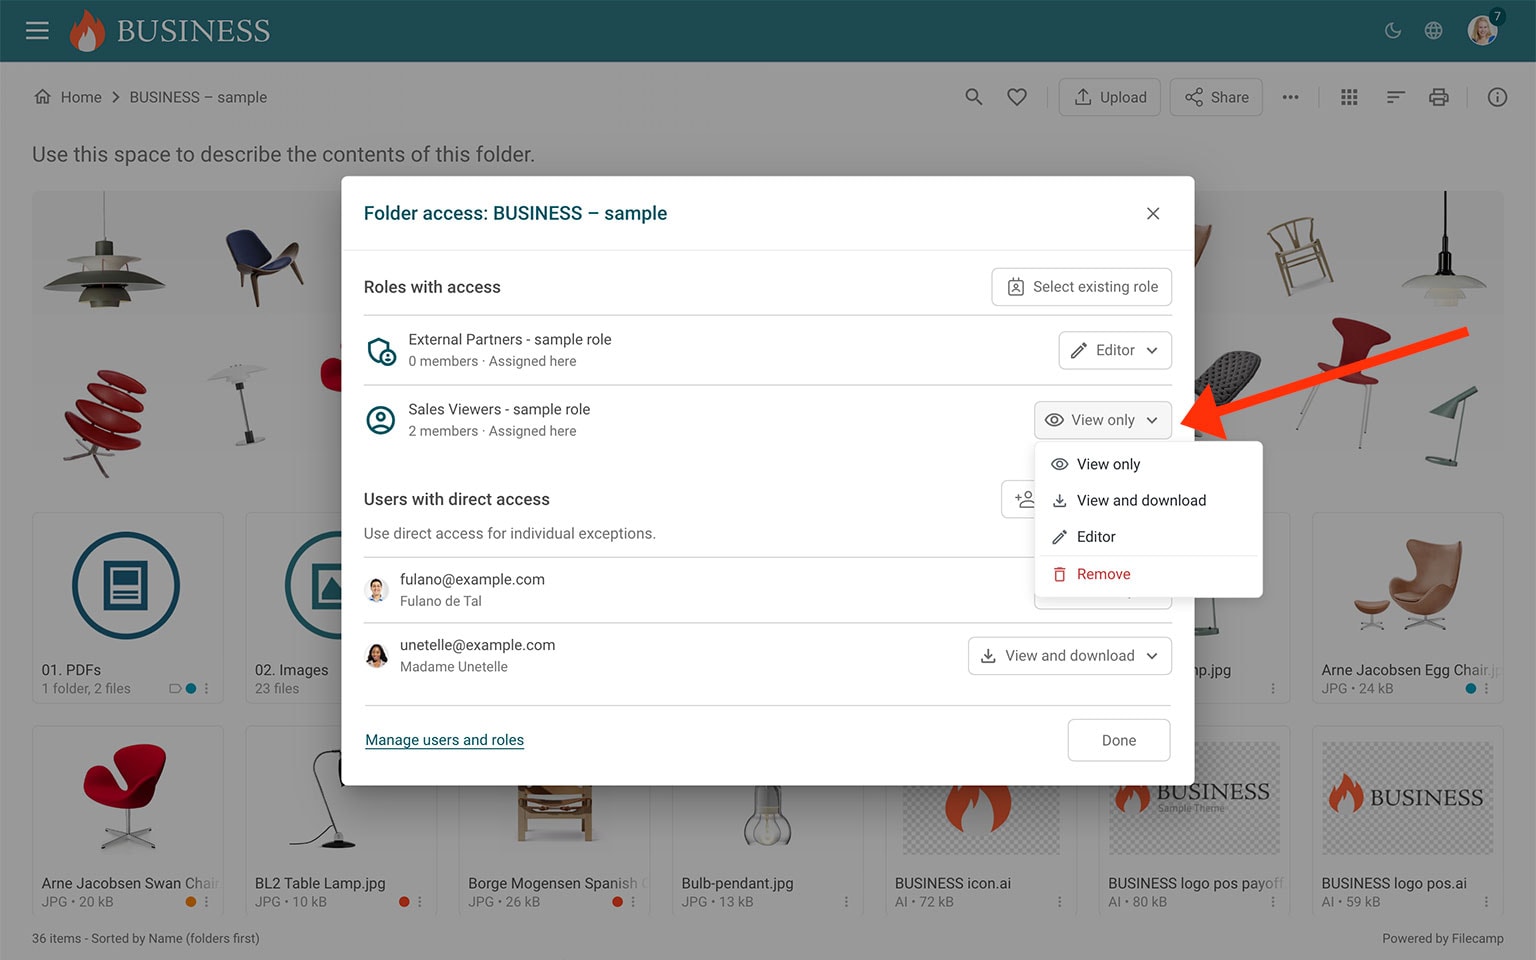
To change what a Role or user can do in the folder, open the Permission set menu next to the Role or user and select another Permission set.
The change applies to the selected folder and any subfolders that inherit access from it.
When you change the Permission set for a Role, the change applies to every user who receives access through that Role.
Add access
You can give access to an existing Role, an existing user, or a new user directly from the Folder access window.
Add a Role
Click Select existing role, choose the Role, and select the Permission set that should apply.
Every user assigned to the Role receives the selected access to this folder.
Add or invite a user
Use direct access for individual exceptions. If the access will be reused, consider using a Role instead.
-
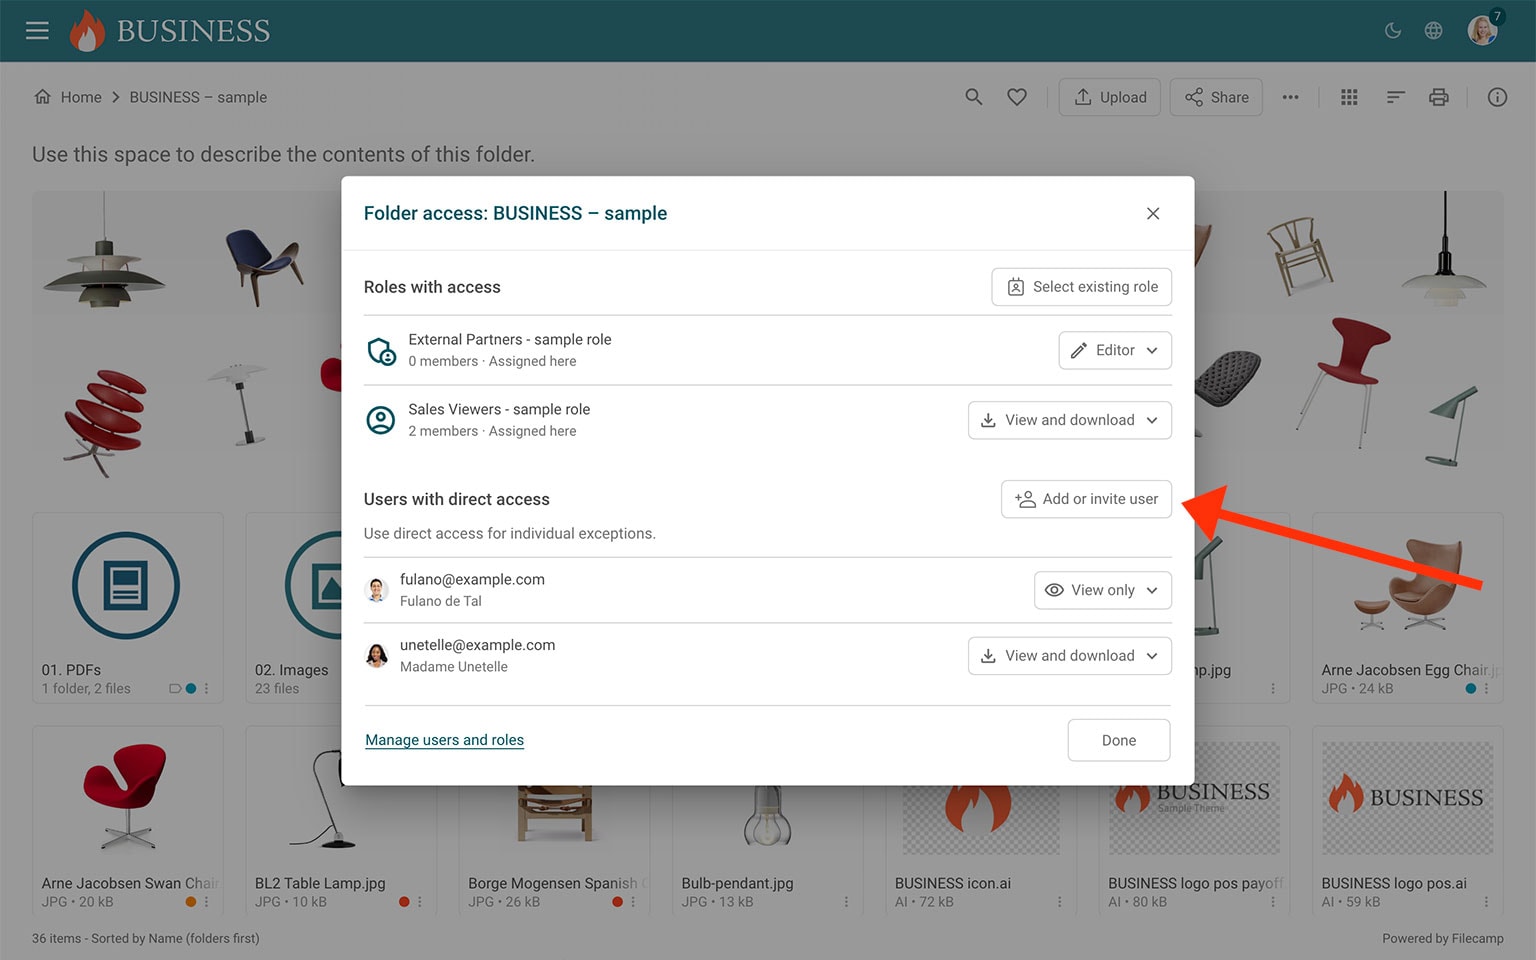
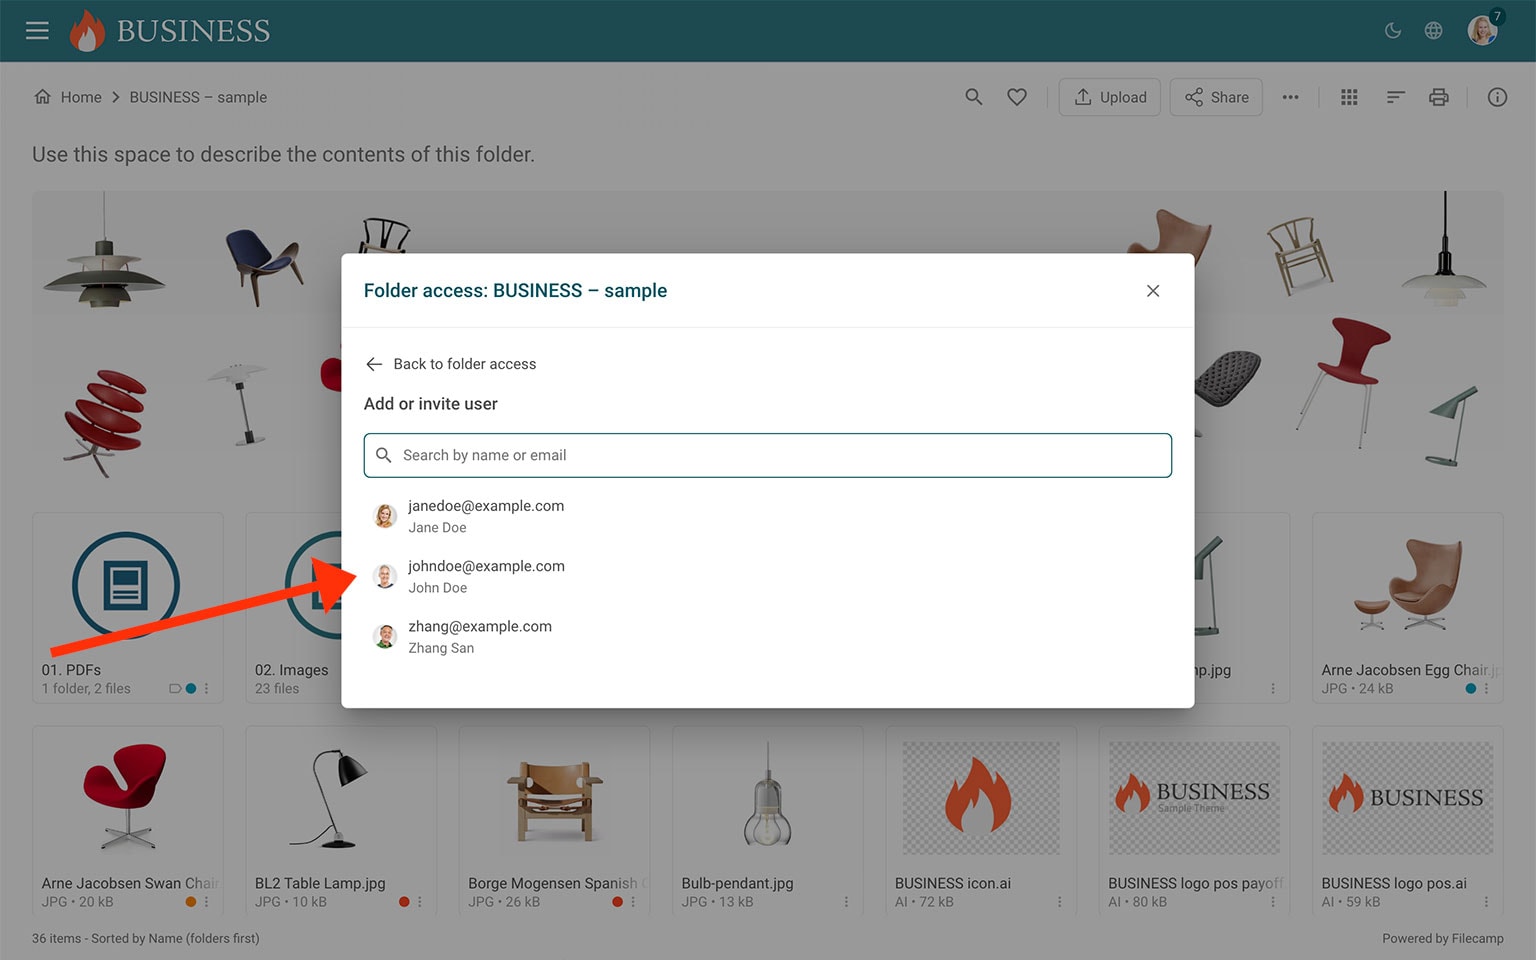
Under Users with direct access, click Add or invite user.
-
Search for an existing user by name or email address.
-
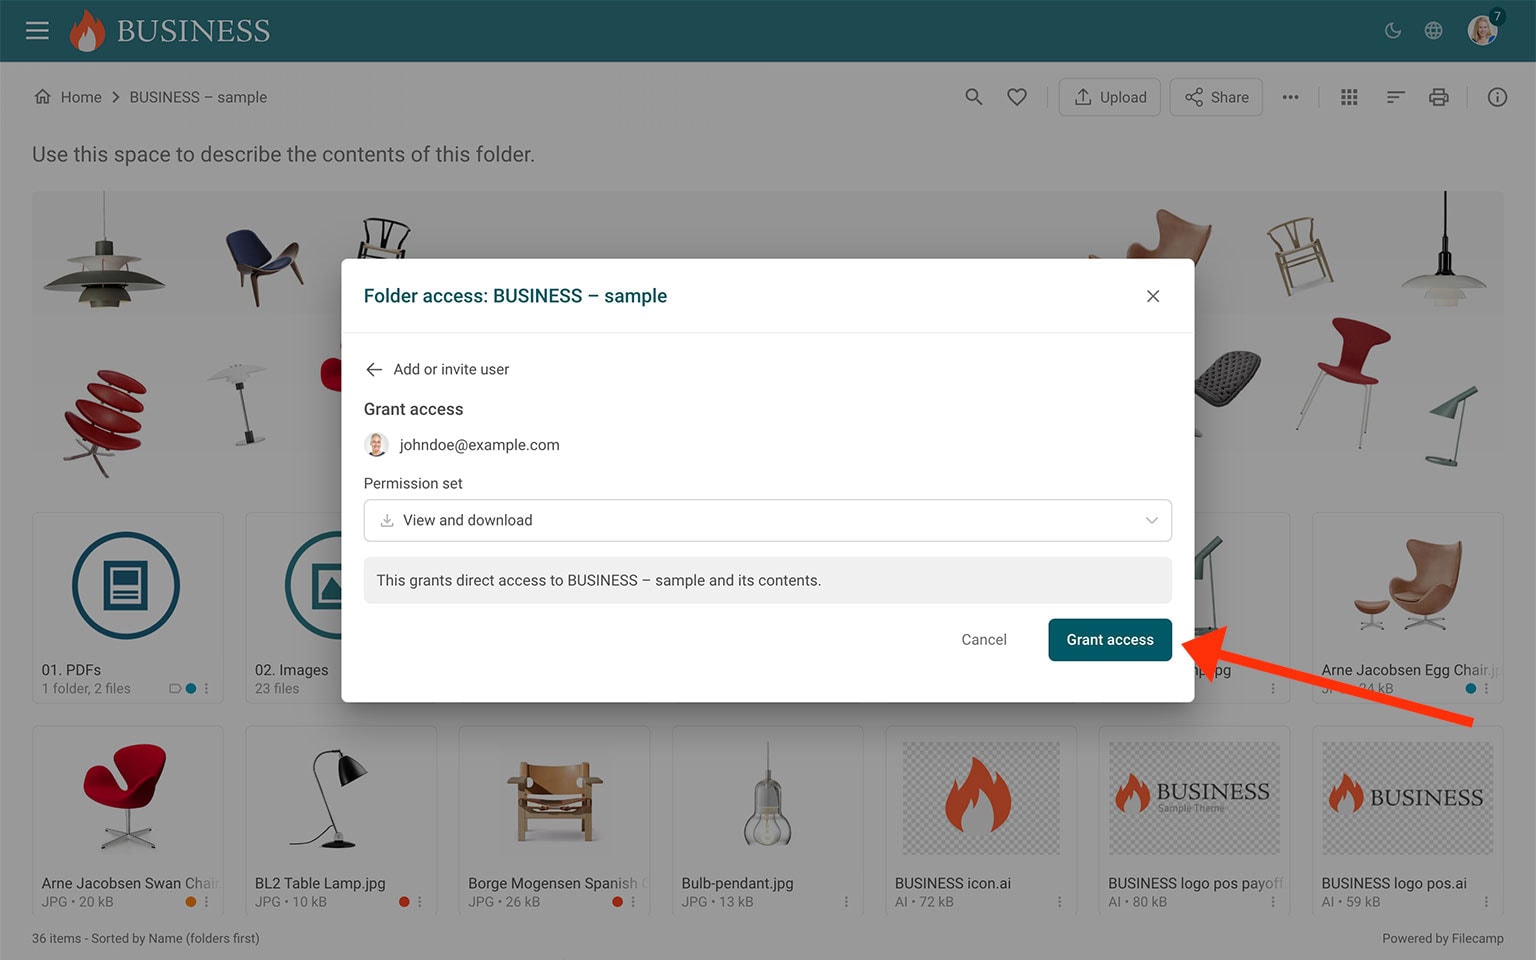
To add an existing user, select the user, choose a Permission set, and click Grant access.
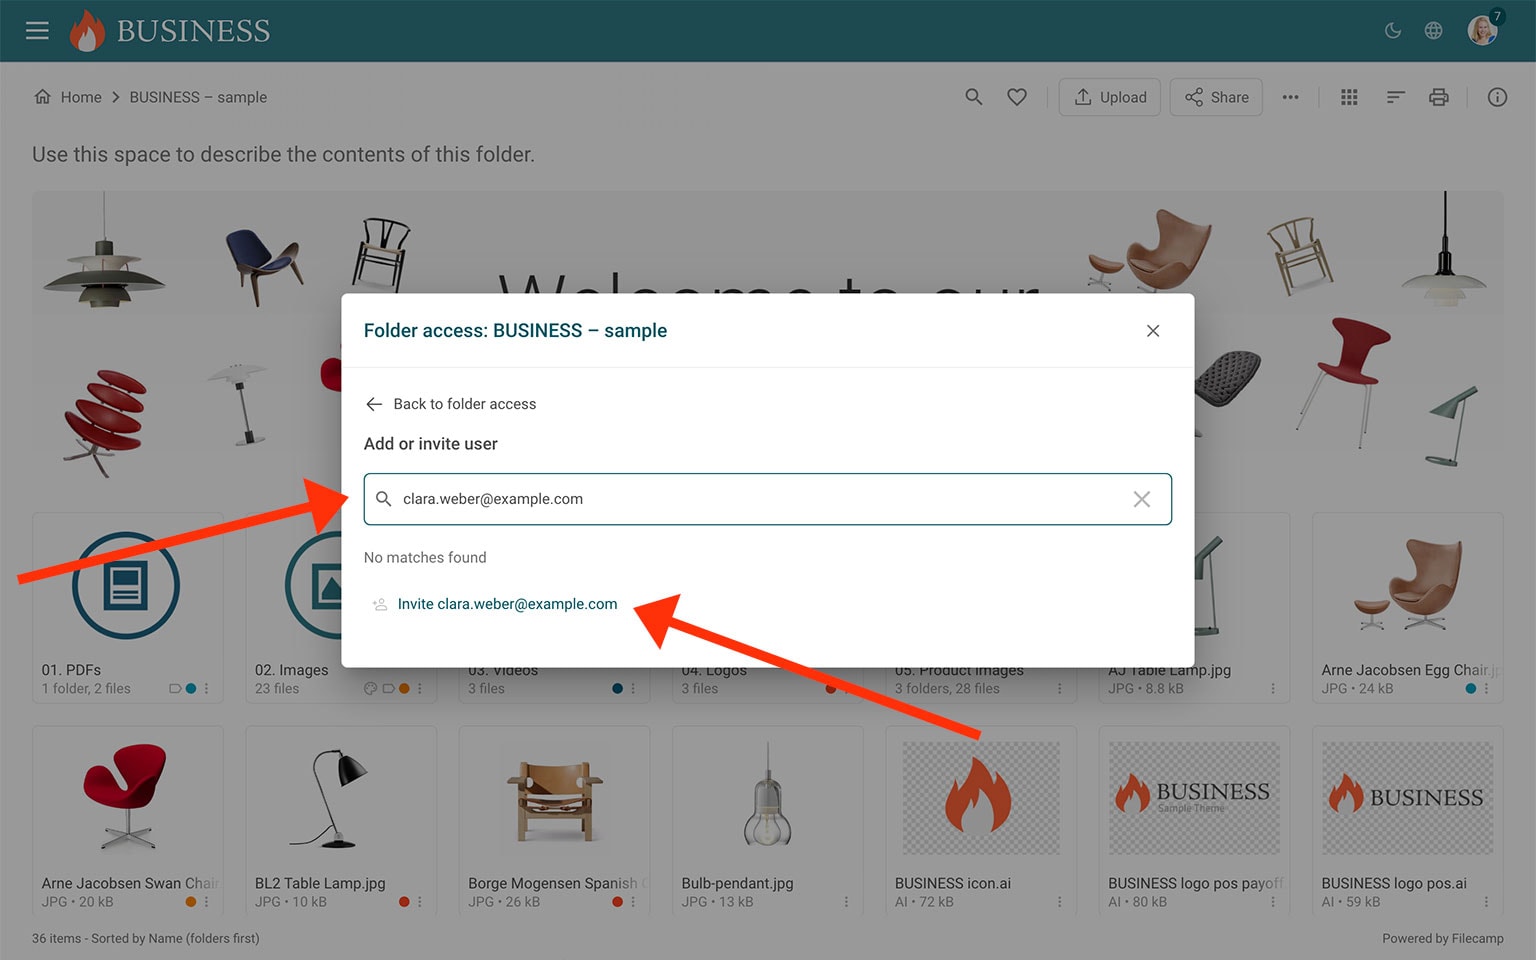
If no existing user matches the email address:
-
Click Invite [email address].
-
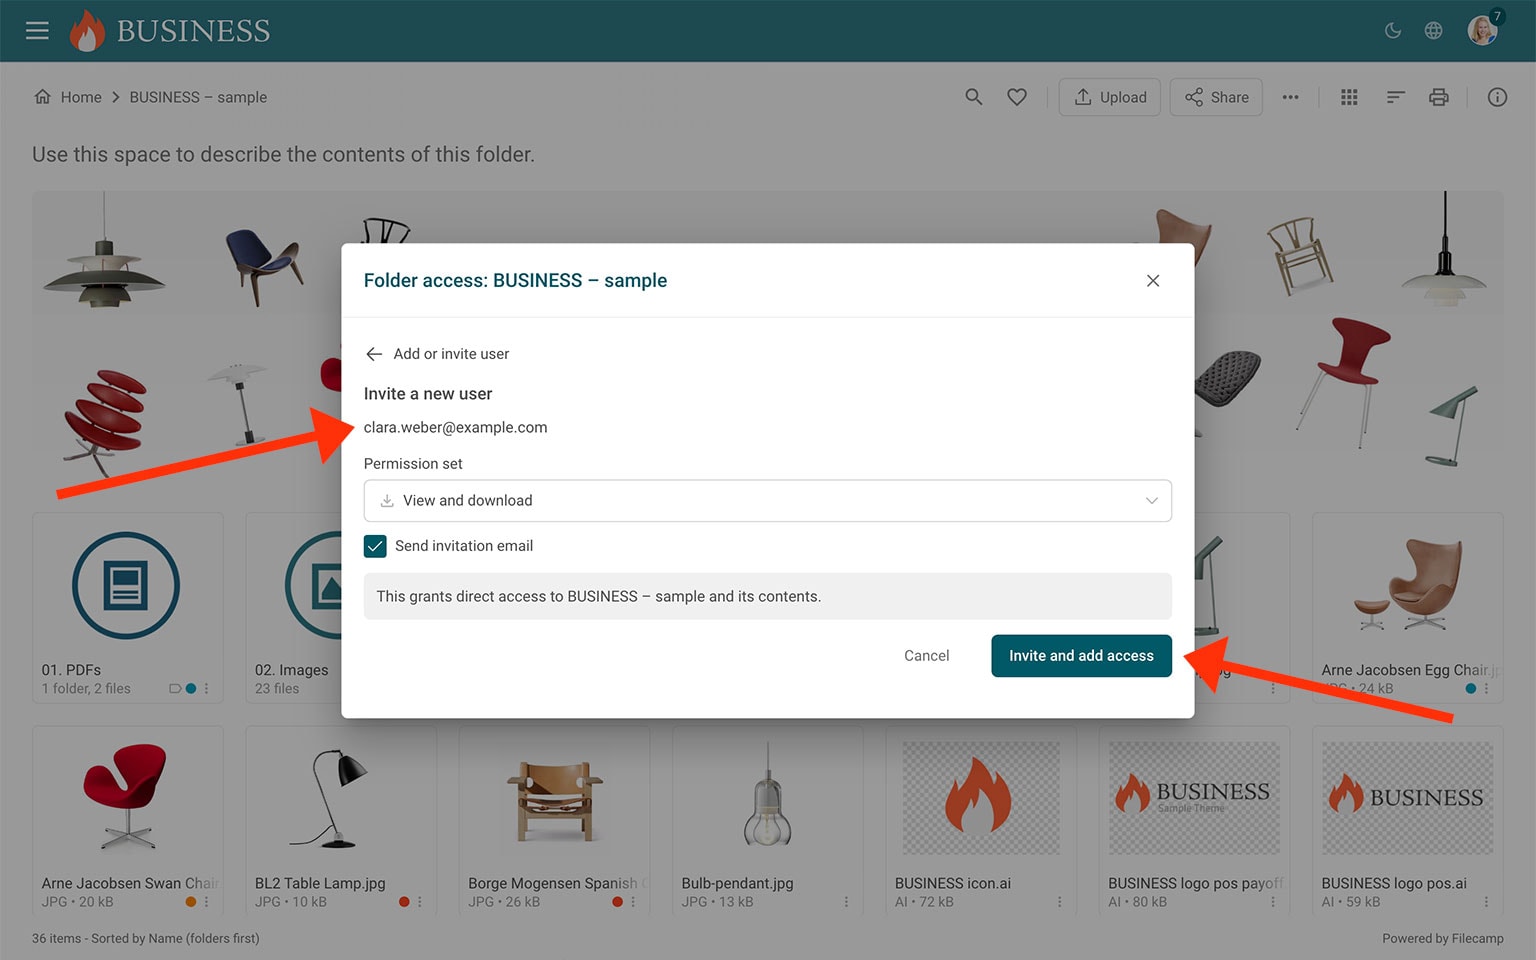
Choose a Permission set. Leave Send invitation email selected if Filecamp should email the invitation, then click Invite and add access.
Remove access
Open the Permission set menu next to the Role or user and select Remove.
Removing a Role from the folder means that users assigned to that Role will no longer receive access to this folder through that Role.
Removing a user from Users with direct access removes only that user’s direct assignment to this folder.
Notice: A user may still have access through another Role, another direct folder assignment, or a parent folder.
Manage users, Roles, and Permission sets
Click Manage users and roles to open Admin > Users.
From there, you can:
- Add, invite, edit, or delete users.
- Create and edit Roles.
- Assign users to Roles.
- Manage direct folder access for individual users.
- Create and manage custom Permission sets from User settings.
Read more about Users, Roles, and Permission sets.
Important notes
Account Owners and Administrators: Account Owners and Administrators always have access to all folders. They are not shown as normal folder permissions.
Roles and direct access can work together: A user can receive folder access through several Roles as well as through direct folder assignments. The permissions from these assignments are combined.
Permission sets: If a custom Permission set is changed, the change applies everywhere that Permission set is used.
Parent folder access: Folder access is inherited by subfolders. Inherited access must be changed in the folder where it was originally assigned.
Inherited controls: If an access control is greyed out, the access is inherited from a parent folder. Hover over it to see where the access can be changed.
No listed access: If no Roles or users have been given access to a folder, only Account Owners and Administrators can access it.